Gareth Shaw, CEO Pera Prometheus
A Security Aspects Letter (SAL) is a written notice from the Ministry of Defence (MOD) telling a supplier, who has a requirement to access and/or safeguard classified assets as part of its responsibility to fulfil a MOD contract, how information assets are classified, and how the MOD expects the recipient to protect them (as a minimum).
A SAL provides a contractual means of ensuring that security is addressed by the Defence Supplier delivering against the contract. Industry Security Notice (ISN) 2026/04, dictates that the SAL must be signed and returned before work starts and that the security conditions applied must be passed down to subcontractors as appropriate.
The obligations a SAL imposes apply to your people, systems, and subcontractors from the day that the SAL is received. The MOD refreshed its guidance in ISN 2026/04 on Security Aspects Letters and Contractual Security Conditions, issued on 17 June 2026. This blog provides guidance on what to do next.
What is a Security Aspects Letter?
A Security Aspects Letter is the MOD’s formal written notice that defines the classified aspects of a tender or contract and the protection each one needs. It matters because your security obligations only become legally effective, once the Contracting Authority (the organisation that placed the contract with you) has given you that notice in writing.
A detailed SAL is usually marked OFFICIAL-SENSITIVE itself, with anything more sensitive in a separate annex. Each new contract gets its own SAL, even where the work continues as an addition to an earlier contract.
The next question is whether your contract needs one.
When does the MOD issue a SAL?
The MOD issues a SAL when any part of a tender or contract is marked OFFICIAL-SENSITIVE or above. Work that is classified OFFICIAL does not require a SAL but the contract security conditions, usually referred to in Defence Condition (DEFCON) 660, still apply. These sit in Defence Conditions (DEFCONs), the standard clauses the MOD puts in its contracts. Under the Government Security Classifications Policy, OFFICIAL-SENSITIVE is OFFICIAL information where the need to know must be reinforced with additional security controls.
| Marking | SAL issued? | Main contract clauses | Facility Security Clearance? |
|---|---|---|---|
| OFFICIAL | No | DEFCON 660 security conditions | No |
| OFFICIAL-SENSITIVE | Yes | DEFCON 660 security conditions | No |
| SECRET and above | Yes | DEFCON 659A (Security Measures) and DEFCON 660 | Yes, if held or worked on at your site |
What must you do when a SAL arrives?
When receive a SAL you are expected to sign and return the acknowledgement before any work begins. In doing so, you confirm your security lead has seen it and the appropriate controls will be applied. Signing the SAL return indicates that you have:
- Read and understood every aspect of the SAL and raised clarification questions to the Contracting Authority and received an answer.
- Challenged anything that looks wrong. You can query a classification without it counting against you and the Contracting Authority must respond promptly.
- Briefed everyone who will handle the material/be involved in delivering the contract.
In the audits we run, the gap I see most often is a SAL, signed by a bid team, that never reaches the person/department running security or IT. A SAL is a contract document and signing it without taking the required action(s) has consequences for the business.
It is strongly recommended that when you receive a SAL that you take the time to study it, and if uncertainties exist, conduct a SAL workshop. Pera Prometheus often assists clients who are new to the SAL process or who have long and complex SALs to run workshops where each aspect of the SAL is analysed. Where ambiguity exists, a SAL assessment is drawn up and a list of assumptions and clarification questions compiled for submission to the Contracting Authority. Studying and understanding the SAL early can save you a lot of trouble further down the line.
Signing a SAL is the easy part but living up to it is harder.
Also, if you hold several SALs you should maintain a SAL register.
Read more: Is a Fractional Security Manager right for your Business
What security conditions come with a SAL?
The security conditions in Annex B of ISN 2026/04 are practical controls the MOD can audit. Guidance on what security controls are required is contained in an Annex to the SAL, however, in broad terms these are
- OFFICIAL-SENSITIVE material locked away, with access to keys and combinations controlled.
- Access limited to people with a need to know who have passed Baseline Personnel Security Standard (BPSS) checks.
- Information marked OFFICIAL-SENSITIVE to be encrypted when sent over the Internet.
- IT systems which are used to handle and store information marked OFFICIAL-SENSITIVE (and above) to have gone through an assurance process which is sanctioned by the Senior Responsible Owner (SRO). Whole disk encryption to be configured on laptops and other portable devices holding OFFICIAL-SENSITIVE information.
- Destruction by approved methods.
The SAL is an additional requirement to DEFCON 658, which requires you to meet Defence Standard (DEFSTAN) 05-138 (Cyber Security Model (CSM)), the MOD’s information security standard for suppliers. Achieving Defence Cyber Certification (DCC) at the correct level is how you demonstrate you meet the CSM standard.
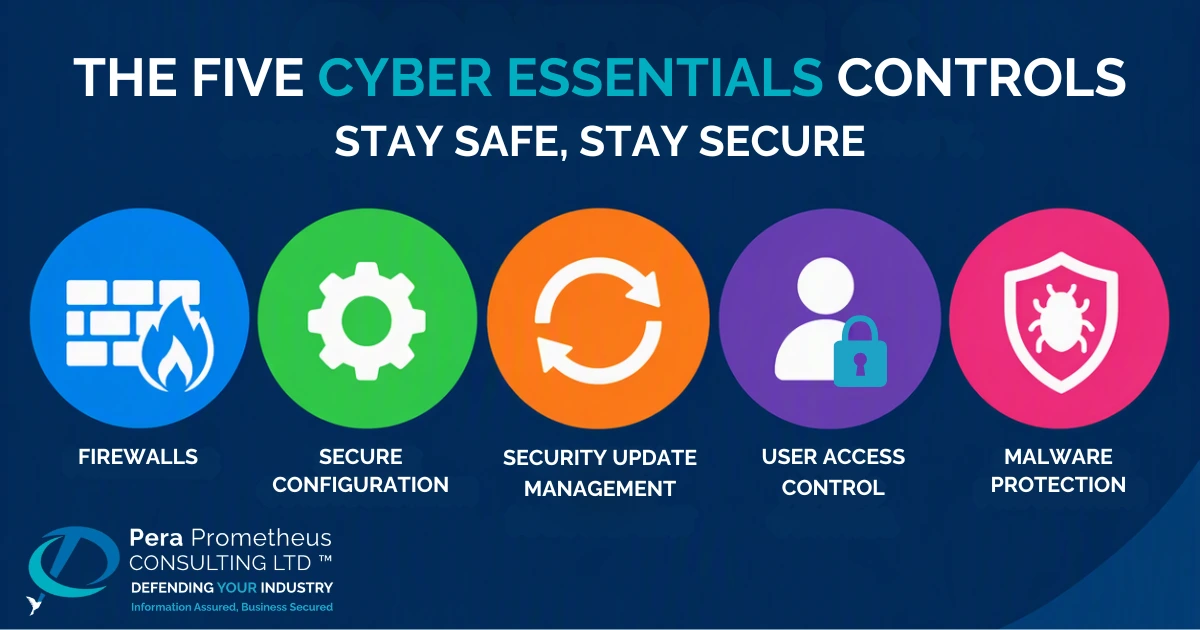
We at Pera Prometheus, are an IASME approved certification body for Cyber Essentials, Cyber Essentials Plus, and DCC Level 0. We also have extensive experience of helping our clients comply with SAL requirements.
One thing that businesses seem to forget is that your own controls are only half the job when others work on the contract with you.
Read more: How to align your DCC Level with MOD contract expectations
Do subcontractors need their own SAL?
Yes, they do if they will access the classified aspects. You pass the SAL requirements down and as their Contracting Authority, you issue your own SAL.
Under ISN 2026/03 on subcontracting classified MOD programmes, sub-contracts where exchanging OFFICIAL-SENSITIVE information, between UK based businesses is involved does not need approval through the F1686 form. However, the F1686 process must be followed where a ned to sub-contact with an overseas business is identified. MOD must give their approval before information exchange takes place..
If a need to share SECRET material with a sub-contractor is identified, the F1686 process must be followed and each party musty have FSC status in place.
The DEFCON 658 Cyber Risk Profile Level must be flowed down as well. Consequently sub-contractors need the right certifications as well as the right paperwork. Once you confirm the SAL’s requirements and flow these down, maintaining the required level of security becomes an ongoing, through-life, contractual reality.
Read more: MOD Requirement to Suppliers: Achieve DCC Level 0 by 31 December 2026
How do you keep a SAL compliant for the life of a contract?
The Contracting Authority must review the SAL at least once a year and at every contract amendment, so check your controls each time this happens. You must also report security incidents to the Defence Industry Warning, Advice and Reporting Point (WARP) within set timescales.
ISN 2025/03 on reporting security incidents treats anything you cannot account for as compromised until confirmed otherwise.
| Priority | Severity | Report to the WARP |
|---|---|---|
| P1 (Red) | Severe | Immediately |
| P2 (Amber) | Serious | Within 24 hours |
| P3 (Yellow) | Moderate | Within 72 hours |
| P4 (Green) | Low | Within 5 working days |
Conclusion
A SAL is where MOD security stops being policy and becomes a contractual obligation with your name on it. Treat it as the start of the work and your commitment, not the end of the paperwork.
Ready to Take the Next Step?
Getting a SAL right across your business and supply chain takes judgement. For a practical view of where you stand, get in touch with Pera Prometheus and we will help you work through it.
Frequently Asked Questions
Q: Is a Security Aspects Letter required for OFFICIAL contracts?
No, a Security Aspects Letter is only issued where parts of the work are marked OFFICIAL-SENSITIVE or above. OFFICIAL contracts still carry security conditions under DEFCON 660.
Q: Can I start work before returning the signed SAL?
No, ISN 2026/04 requires a signed SAL acknowledgement before any work begins.
Q: Does a SAL replace DEFCON 658 and the Cyber Security Model?
No, a SAL works alongside DEFCON 658 rather than replacing it. The SAL defines the classified aspects, while DEFCON 658 sets the information security controls for the MOD supply chain, through the Cyber Security Model and Defence Standard (DEFSTAN) 05-138.
Q: How quickly must a security incident be reported to the MOD?
A severe (P1) security incident must be reported to the Defence Industry WARP immediately, and a serious (P2) one within 24 hours. Moderate and low incidents allow 72 hours and five working days.
Q: Who do I contact if my SAL is unclear?
Contact your Contracting Authority first, as it issued the SAL and must respond to queries promptly. For wider ISN questions the ISAC can be reached at [email protected]. Equally, expert consultants like Pera Prometheus can also help if required.
Stay Safe, Stay Secure