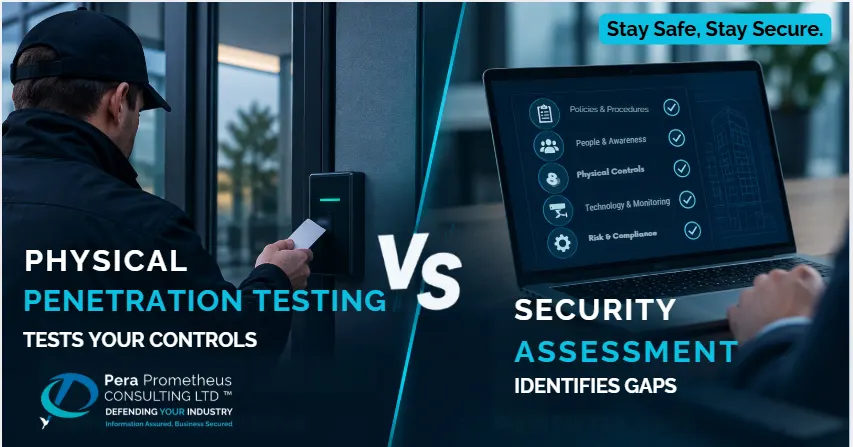
Physical penetration testing vs security assessment comes down to what you are trying to achieve. A security assessment checks your physical controls against a standard, with your team’s help and shows what is missing. A physical penetration test is an authorised intrusion attempt emulating real-world methods, used by malicious threat actors to compromise and undermine your physical security controls intended to prevent unauthorised access. Ideally, a business should conduct the assessment first, then conduct a physical penetration test after remediation actions are completed.
Think of it this way; remember the security breach at RAF Brize Norton back in June 2025? A Physical Assessment/Assessment would have asked “Does the Site have a perimeter fence?”, a Physical Penetration Test would have actively looked for the weaknesses in the perimeter fence that the attackers exploited.
A Security Assessment checks that your security measures are in place, a Penetration Test checks whether they actually work.
Organisations and businesses need to understand that an assessment and a physical penetration test answer different questions and suit different stages of a site’s life. For a security controller or facility lead, the wrong choice can be a waste of money and perhaps, worse still, offer a false degree of confidence that your physical security arrangements are adequate. This blog aims to clarify the differences between the two to allow an informed decision.
What is a physical security assessment?
A physical security assessment is a planned, open review of your site’s physical controls against a set standard or your own security policy. Your team knows it is happening and assists the assessmentor with its completion.
The assessmentor walks the site, reviews your procedures and checks your records. Typical areas that assessments assess are the perimeter, door access, visitor handling, alarms and secure storage. The output of the assessment is a list of gaps, ranked by risk. Government Functional Standard GovS 007: Security, Version 2.0 (issued 13 September 2021), is written for government organisations. It expects physical security requirements to be set through risk assessment. The National Protective Security Authority (NPSA) guidance on Protective Security Risk Management sets out eight steps. An assessment identifies what should be there, in terms of controls i.e. locks, alarms, sensors, CCTV etc. however, it does not establish how effective these controls are against a malicious actor.
If your procedures are still formative, read our post on how a Security Management Plan prepares defence suppliers.
What is physical penetration testing?
Physical penetration testing is an authorised, physical attempt, emulating the activities of a malicious actor, to gain unauthorised access to your site. Penetration testers will conduct preliminary Open Source Intelligence gathering to obtain information on the target, undertake reconnaissance of the site to observe behaviours, identify patterns etc. before making an attempt to gain unauthorised entry. The attempt may involve social engineering of your staff (encouraging them to unknowingly assist the breach attempt). There is National Cyber Security Centre (NCSC) guidance on penetration testing Penetration testing | National Cyber Security Centre, which is written for IT systems. It describes a test as trying to breach security “using the same tools and techniques as an adversary might”. The NCSC also says a penetration test “should be thought of as similar to a financial assessment”. In my view the same thinking applies to buildings. Your team runs security day to day and the test checks that their procedures work. That is a different job from a physical security assessment.
Legitimate, professional Physical Penetration Testing will always be conducted to achieve specified objectives and methods agreed between the organisation and the testers who will operate under a Letter of Authority (LoA) first. Our own physical penetration testing service starts with it. Some organisations are hesitant to conduct physical penetration tests as they are concerned about commercially sensitive loss or physical damage – this will not occur when conducted by professionals and the scope of the assessment will always be clearly defined under contract scope and the LoA.
What is the difference between a physical penetration test and a security assessment?
A security assessment establishes whether the correct controls exist. A physical penetration test validates how effective these contrtrols actually are.to stop an intruder. Neither should replace the other, which is why getting it done in the right order is important.
| Physical security assessment | Physical penetration test | |
|---|---|---|
| Question answered | Are the right controls in place? | Do the controls work? |
| Method | Open review of site, documents and records | Simulated intrusion, open or covert |
| Who knows | Staff are told and take part | A small group of senior people |
| Measured against | A standard or your own policy | An agreed scenario and targets |
| Output | Gaps ranked by risk | How far the testers got and how |
| Best timing | Early, then at regular intervals | Once assessment gaps are closed |
Which one do you need first?
Most sites should conduct an assessment first. A test against a site with known gaps tells you little that is new. The working rule for Pera Prometheus is this:
- New site, new contract or first clearance requirement: start with an assessment.
- Controls in place and assessment gaps closed: run a physical penetration test.
- After a security incident or a major site change: do both, assessment first.
Does Facility Security Clearance require a physical penetration test?
No. The published policy for Facility Security Clearance (FSC) does not mention physical penetration testing. FSC, formerly known as List X, is the Ministry of Defence (MOD) assurance that a contractor’s site can protect classified material.
The FSC Policy and Guidance, version 1.4, dated March 2024, gives the assurance role to the Industry Security Assurance Centre (ISAC). ISAC is the MOD team that gives security guidance to defence contractors. Its assurance visits are repeated every two years where assets up to SECRET are held and annually where TOP SECRET assets are held. The policy also makes your Facility Security Controller responsible for monitoring security controls.
Assessments and tests support that monitoring duty. Both are voluntary and both help you find weaknesses before an assurance visit does. If the site holds classified material, the company will need to speak to their ISAC Security Advisor before planning a test.
Read more: what Facility Security Clearance is and when you need it and how List X became FSC.
Conclusion
An assessment and a physical penetration test are not rivals. One tells you whether the right controls are in place and the other validates the efficacy of them. Assessment first, fix what you find, then test.
Frequently Asked Questions
Q: What is the difference between a physical penetration test and a physical security assessment?
A physical security assessment checks whether the right controls are in place against a standard, while a physical penetration test checks whether those controls are effective in stopping a simulated intrusion attempt. The assessment is open and the physical test is usually covert.
Q: Is physical penetration testing legal in the UK?
Physical penetration testing should only go ahead with the written authorisation of the site owner or custodian. Take your own legal advice where ownership or occupancy is shared. Always have a LoA in your possession before conducting a physical assessment.
Q: How often should physical penetration testing be done?
There is no one answer to this question, it depends upon a number of variables. The best way to identify intervals between tests is to discuss the requirement with professionals.
Q: Does a physical penetration test include social engineering?
A physical penetration test usually includes social engineering, which means persuading staff to break the rules. Following staff through doors (tailgating) and impersonating facility management staff to bypass reception are common examples, where the agreed scope allows them.
Q: Do I need a physical penetration test for Facility Security Clearance?
A physical penetration test is not mentioned in the published Facility Security Clearance policy, version 1.4. ISAC assurance visits are the formal check and a test is a voluntary way to prepare. If you did want to conduct a physical penetration test of a secure facility it is essential that sensitive information is protected at all times and compromises cannot take place.